

Attackers are impersonating popular AI brands like Perplexity, Claude, ChatGPT, and Copilot to spread information stealers, backdoors, malicious browser extensions, and other malware, according to Sophos.
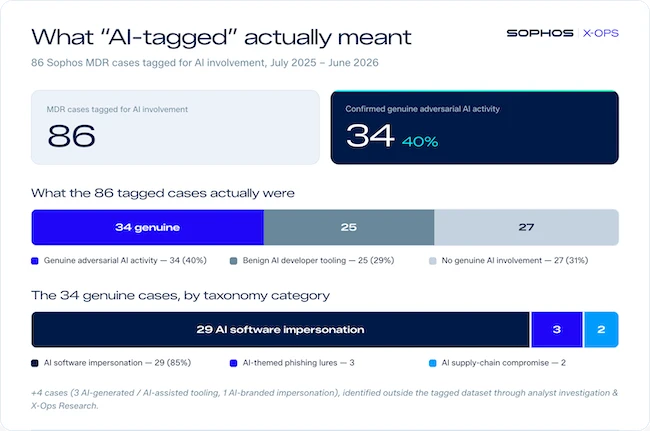
Overview of MDR cases with AI involvement (Source: Sophos)
Sophos X-Ops reviewed 12 months of managed detection and response cases, covering July 2, 2025 through June 29, 2026. Of 86 cases initially tagged for AI involvement, 34 were confirmed as malicious activity involving AI. Researchers added four cases uncovered during separate investigations, bringing the dataset to 38 incidents.
In 35 cases, criminals targeted AI products, brands, or their surrounding ecosystem. Software impersonation accounted for 30 of the 38 incidents. Claude was the brand attackers reached for most often, showing up in 26 of the cases reviewed.
Fake Claude installers push malware
Many of the incidents involved InstallFix, a spin on the well-known ClickFix technique.
“Whereas ClickFix attacks mimic an error or verification step, such as a fake CAPTCHA, an InstallFix page may present a polished, step-by-step installation guide. Both end with the user copying and running (often obfuscated) commands that ultimately result in a malware infection,” researchers wrote.
In one case, a fake Claude site walked the victim through an mshta command that pulled a payload from a lookalike domain. The download was packaged as a Windows app named “claude” or “claude.msixbundle.” Once run, it fetched code that executed in memory and tried to hollow out browser processes. Other variants included a booby-trapped Claude Setup.zip archive and a repackaged claude.exe that functioned as a malware loader.
“From a defensive perspective, in the impersonation cases we reviewed, the decisive protections were based on conventional delivery and payload behaviors, rather than AI-specific characteristics,” researchers added.
“The earliest and best defense remains unchanged: install AI tooling only from confirmed vendor domains.”
Extensions with fake reviews to match
Sophos found several browser extensions posing as AI assistants, including one marketed as “AI Sidebar with DeepSeek, ChatGPT, Claude,” that functioned as infostealers and communicated with command-and-control infrastructure.
One case involved four customers who installed a fake Perplexity extension distributed through the Chrome Web Store. It hijacked searches, rerouted them through a lookalike domain, and sent browsing data to attacker infrastructure in real time.
On the Chrome Web Store, the listing had a 4.7-star rating across 67 reviews and a 10,000-user install count, which Sophos said could give it the appearance of legitimacy.
Attackers turn to AI for malware development
In another case involving a financial services organization, Sophos found what it calls the “clearest case of AI-generated attack tooling” in its data. The attackers initially compromised a custom PHP application through SQL injection.
During the investigation, researchers discovered a remote access Trojan that communicated through Slack. They linked the malware to a public GitHub repository whose commit history showed a human account working with a Claude coding agent.
Written in Rust, the malware polled a Slack channel for commands. Its planned capabilities included executing commands, retrieving files, downloading configuration data, establishing persistence through a scheduled task, and, at one stage of development, opening a reverse shell. The repository’s commit history showed that development took place over several days.
Researchers also encountered possible signs of AI-generated code during a separate ransomware investigation. The attack tooling contained unusually detailed comments and structured PowerShell code, though Sophos said these characteristics were circumstantial evidence and did not establish that AI had been used.
Sophos found nothing in its own telemetry to suggest AI is running attacks on its own. “Where we have seen attackers genuinely use AI as a capability, it sat at the lightest-touch end of the scale, in the AI-generated sub-category, with a human in control,” they concluded.
