


VulnOps is quickly becoming a core security function. Its purpose is straightforward: continuously identify, prioritize, fix, and verify software vulnerabilities before they turn into exploitable risk.
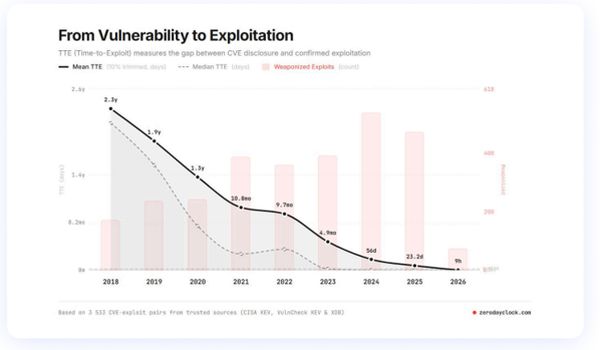
Like DevOps and Site Reliability Engineering before it, VulnOps brings a flow-based operating model to a process that has often been slow, ticket-driven, and reactive. That shift is especially important after Mythos, because AI-driven vulnerability discovery now moves faster than traditional patch cycles can support.
Following the Cloud Security Alliance’s April 2026 briefing, the message is clear: organizations can no longer manage vulnerabilities as a periodic backlog. They need a permanent VulnOps capability with owners, workflows, automation, and metrics.
 The baseline imperative for VulnOps
 The baseline imperative for VulnOps
The old model is simple: scan, ticket, rank by CVSS, and patch on a monthly or quarterly schedule. The problem is that this process assumes the queue stays relatively stable (and it doesn’t). But VulnOps assumes a continuous stream of AI-discovered vulnerabilities requiring permanent triage.
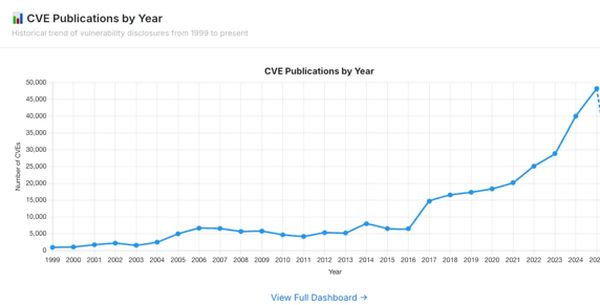
The numbers show why the old process is breaking. Last year alone, more than 48,000 new CVEs were published. This volume forces a move away from periodic sprint mentalities toward building permanent prioritization and remediation capacity. Yet, any continuous remediation effort requires a clear understanding of the environment first.
 “Both security and IT share the same foundational goal: knowing what normal looks like. Security is anomaly detection. IT is troubleshooting. Neither works without an established baseline,” Jason Kikta, Automox CTO, said.
You simply can’t secure systems you don’t fully understand.
The human cost and staffing reality
Maintaining a continuous patching flow carries immediate staffing implications. Security teams are absorbing exponential workload increases, often without corresponding investments in automation or tooling. The recent CSA briefing treats team resilience as a strategic priority. It explicitly recommends that organizations increase headcount alongside automation initiatives to prevent widespread burnout.
The manual burden is a documented reality. According to the 2026 State of Endpoint Management Report, 43% of teams spend 10 or more hours per week on manual endpoint tasks. Despite this drain on resources, 27% of organizations still allocate less than 10% of their IT budget to endpoint management. More concerning, only 6% of organizations report being fully automated.
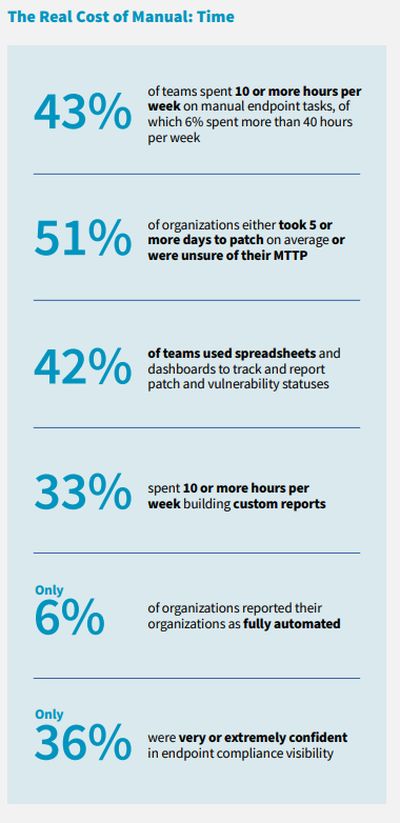 Relying on manual intervention to process a machine-speed vulnerability feed guarantees that teams will eventually fail to keep pace. This exposes organizations to unnecessary risk while exhausting their specialized personnel.
Building the operational foundation with autonomous endpoint management
A VulnOps agenda relies heavily on endpoint management to succeed. A complete and accurate endpoint inventory acts as the mandatory precondition for this operational model. You can’t patch, segment, or measure service-level agreements for assets you don’t know exist. Transitioning from manual oversight to an automated framework is necessary to establish this baseline.
To implement this, tools like Automox provide autonomous endpoint management mechanisms. Automox’s Turnkey Results operates as a personalized blueprint built from 1.4 billion policy runs, providing an implementation design specific to each environment. This moves organizations from relying on ad-hoc scripting to governed execution at frontier pace.
The financial and operational return on building this foundation is measurable. Recent 2025 data demonstrates a 362% return on investment with a four-month payback period for automated patch and endpoint management. Structured automation directly offsets the rising costs of continuous remediation.
Rethinking remediation metrics
VulnOps changes how security teams instrument their programs. Rather than relying on severity ranking alone, a mature VulnOps function measures lead time from disclosure to verified remediation, change-failure rates on patches, and pipeline saturation.
Depending exclusively on CVSS scores is dangerous. Following the National Vulnerability Database’s recent triage policy shift, the majority of new CVEs will arrive without full enrichment.
To adapt, VulnOps programs are transitioning to composite signals. They combine the CISA Known Exploited Vulnerabilities (KEV) catalog and the Exploit Prediction Scoring System (EPSS) to determine what actually requires immediate automated remediation. This data-driven approach ensures teams allocate their automated patching cycles to active threats. It reduces noise and focuses execution on defects that present immediate, provable risk.
Turning continuous remediation into practice
The CSA briefing turns this shift into a concrete roadmap. Organizations should begin immediately by checking that known vulnerabilities are patched and baseline configurations are in place. The focus should move to automating routine remediation and finishing asset inventories within 45 days.
The longer-term target is clear. VulnOps should operate as a dedicated function with staffing and ownership as well as metrics within 12 months. Achieving operational readiness means acknowledging that vulnerabilities won’t ever stop flowing. Building a continuous, automated response is the only sustainable strategy moving forward.
