

A successful multi-agent AI attack on a government’s agencies in the Asia-Pacific region by a Chinese-language operator has put nations and businesses on notice that near- and fully-autonomous AI-enabled attacks are now a reality.
The attack used as many as eight simultaneously-operated AI agents to conduct reconnaissance, find and evaluate vulnerabilities, attack networks and systems, and then evaluate and improve successive attacks, according to research from sovereign AI firm Dream published on Aug. 12. The company did not attribute the attack to a specific actor or group, but researchers did point to strong evidence that the attackers spoke simplified Chinese — typically a sign of speakers from mainland China.
While the company also limited the identification of the targets to “government entities in Asia,” Taiwan’s Ministry of Digital Affairs (MODA) issued a statement the following day, giving details of its response to an attack matching much of Dream’s description, including that it used “AI agents like OpenClaw.”
Overall, the incident should be a warning that fully autonomous attacks could be used against major targets, says Amir Becker, chief business and strategy officer at Dream and a former commander of the cyber operation division of Israel’s 8200 Unit, more formally known as the Central Collection Unit of the Intelligence Corps.
“The speed and the scale of the attacks are changing and the economics of cyberattacks are changing dramatically as well,” he says. “The defensive side of the house … cannot continue … just running [operations using] humans. If the attackers are using AI to attack, the defensive side must adapt the same attitude and direction at the same scale and speed as well.”
Automated attacks have quickly risen as a concern for governments and large enterprises. Between December 2025 and February 2026, attackers targeted the Mexican government using an automated attack with AI capabilities, but that attack failed in many ways. The more recent attack on Hugging Face by OpenAI AI models is a fully automated examples of what an agent-based attack framework can do: The frontier model used agents to escape the company’s sandboxed research environment by finding a previously unknown vulnerability in a package manager and creating a tool to exploit the issue.
AI With a Bayesian Brain
In the latest incident investigated by Dream, attackers used standard social engineering tactics to bypass the guardrails of unidentified frontier models to create a penetration testing framework to attack a government agency in an unidentified Asian nation, according to Dream. The researchers based their analysis on an operational workspace consisting of over 160 megabytes and 1,395 files, the Dream research advisory stated.
The attackers’ AI operations were built on top of the OpenClaw and Hermes agentic frameworks, using up to eight subagents, each using a single letter “A” through “Q.” The subagents were each tasked with autonomously executing part of the attack chain, including cracking government employee credentials, identifying and exploiting vulnerabilities, exfiltrating personnel records, and installing persistent backdoors on government Web applications, the researchers stated.
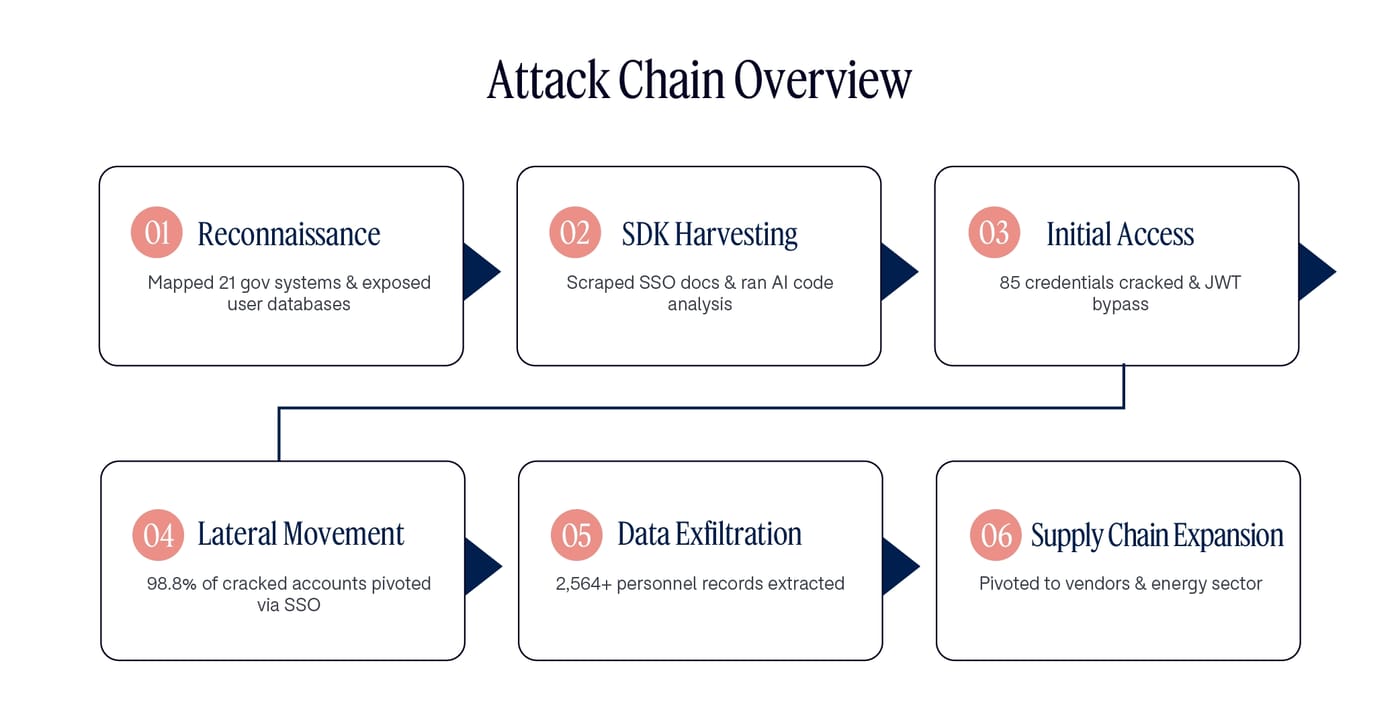
The AI agents followed an attack chain familiar to any human analyst or attacker. Source: Dream
“Each agent had a different responsibility — for example, one agent could be responsible for doing the exploration of APIs for open endpoints, while another agent maybe was responsible for credential theft,” a Dream cybersecurity researcher told Dark Reading, requesting anonymity for security reasons. “The main parent session was responsible for coordinating the sub-agent, so each wave could run several sub-agents.”
In total, there were 12 attack waves. The coordinating agent used a simple Bayesian scoring algorithm to give points to successful agent findings, and penalized unsuccessful ones, taking actions based on those scores.
Taiwanese Attack Showed Signs of AI
The likely target appears to be Taiwan, as first identified by the Financial Times.
On Aug. 13, Taiwan’s MODA acknowledged that its “cybersecurity monitoring units detected abnormal attacks targeting government agencies” in July. Internally, MODA and the National Institute of Cyber Security (NICS) issued alerts and launched investigations into the attacks on July 20 and had completed its investigations by Aug. 13, MODA stated in its Chinese-language announcement (via Kagi translate).
“Investigation results show that this wave of attacks has clear characteristics of overseas origins, utilizing a hybrid model where hackers combine operations with AI agents like OpenClaw,” the statement said. “AI agents can rapidly chain multiple attack methods and use secondary systems — such as backup or testing environments — as springboards, making the attacks fast, low-cost, and large-scale.”
While Dream declined to confirm Taiwan as the target — citing the need to protect its clients — the timeline appears to fit. The threat actors launched their attack against a government target in the Asia-Pacific region over four days — July 1 to 4 — and initial signs of the attack were detected by the Dream research team on July 2. The initial discovery, the company’s investigation and resulting notification of the affected government agency, and the government’s own investigation could account for the more than two-week difference between the end of the attack and the July 20 alerts issued by Taiwan’s cyber-response agency.
“We first identified the activity on July 2nd and continued to monitor and investigate it in the following weeks to fully understand the scope of the operation,” Dream’s research team said in a statement to Dark Reading in response to questions on the discovery timeline.
Dream tracks more than 100 threat groups, but could not definitively link any of those groups to the tactics, techniques, and procedures discovered in the attackers’ workspace, the company said.
A Warning for Organizations in Asia — and Worldwide
The attack should worry not only Asian governments, but global organizations as well, says Carl Wright, chief commercial officer at cybersecurity firm AttackIQ, and former chief information security officer (CISO) for the US Marine Corps. China’s “order of operation” typically is to use capabilities against rivals and adversaries in its sphere of influence, and then expand beyond that, he says.
“China may release some incremental capabilities to their sphere in Asia to test, prototype and make better those capabilities before they come against organizations that maybe are farther along in their journey from operational capability,” he says.
Wright says countries such as Taiwan and South Korea are “easy targets for not just China, but North Korea or any crime syndicates that want to practice their capabilities before they come to maybe more of a tier-one operator in the UK, US, other countries that have been developing capabilities and investing [in cyber defense] at a much higher and faster pace.”
Companies should take a page from attackers’ playbooks. The threat actors in the latest case built an AI attack framework, but in order to bypass the AI guardrails, claimed they were conducting legitimate pen testing activities. Defenders should do the same thing, but in their case, they would be using the AI framework for legitimate pen testing, the Dream researcher tells Dark Reading.
“Let’s start building agents just like attackers do, and try to find how an attacker would attack us, then of course, we can defend in the same way,” the researcher says. “We basically need to think like the modern attacker in the era of AI and think how an attacker would leverage AI to attack us.”
The researcher also points out that the attack required no zero-day exploits, highlighting the need for organizations to do better at closing basic gaps.
Until defenders aggressively adopt AI to combat AI-driven attacks, the asymmetry in capabilities between attackers and defenders will only grow, Wright says.
“We used to say that if the adversary spends a dollar on an attack, we’d have to spend $100 to defend against it,” he says. “The fundamental problem now is that the adversary has to spend five cents, not a dollar. The asymmetric aspect of the cost of them producing attacks and us defending is a growing gap because we’re not using AI fast enough on the defender side.”
