
LIVE NEWS
  • Trump dangles $500 ACA refund checks, but legal basis is unclear
  • Guest post: How extreme heat is ‘creeping’ from summer into autumn and spring
  • Musk threatens to sue filmmaker Alex Gibney for defamation : NPR
  • 25 Years After 9/11, What Makes a Good Counterterrorism Strategy?
  • Twenty-five years after 9/11, strategic shocks mustn’t cloud strategic thinking
  • Infectious diseases will seed new ground as the planet warms — here’s where they’ll spread
  • India crypto takedowns target 15 platforms
  • NFL’s Rams and 49ers head to Australia in international expansion
Prime Reports
  • Home
  • Popular Now
  • Crypto
  • Cybersecurity
  • Economy
  • Geopolitics
  • Global Markets
  • Politics
  • See More
    • Artificial Intelligence
    • Climate Risks
    • Defense
    • Healthcare Innovation
    • Science
    • Technology
    • World
Prime Reports
  • Home
  • Popular Now
  • Crypto
  • Cybersecurity
  • Economy
  • Geopolitics
  • Global Markets
  • Politics
  • Artificial Intelligence
  • Climate Risks
  • Defense
  • Healthcare Innovation
  • Science
  • Technology
  • World
Home»Cybersecurity»Hackers infect Android car head units with proxy botnet malware
Cybersecurity

Hackers infect Android car head units with proxy botnet malware

primereportsBy primereportsAugust 22, 2026No Comments3 Mins Read
Share Facebook Twitter Pinterest LinkedIn Tumblr Reddit Telegram Email
Share
Facebook Twitter LinkedIn Pinterest Email


Hackers infect Android car head units with proxy botnet malware

A supply-chain attack targeting Android-based car head units is using a legitimate device-update app to spread malware that enlists compromised devices in a proxy botnet or uses them for ad fraud.

Kaspersky researchers analyzed the malware and attributed the operation to the MoYu group, a threat actor previously associated with the BadBox malware botnet.

The researchers note that this is the first documented case of a malware infection chain specifically created for the targeted car head unit.
image

MoYu’s operation targets systems from DoFun, a Chinese automotive software and hardware provider owned by Shenzhen Driving Control Technology Co., Ltd.

DoFun is an automotive software, cloud services, and hardware provider that sells generic Android-based head units, which act as the command center for a car’s infotainment, navigation, and settings systems.

In June, Kaspersky researchers found a rogue APK file being downloaded from a legitimate DoFun system app, TWCore, which receives instructions through an MQTT server hosted at cardoor[.]cn.

The unknown app has no interface and is a piece of malware called JarService. When launched, the malware decrypts and executes a second-stage loader that establishes communication with a command-and-control (C2) server and downloads another encrypted payload.

The final payload periodically reports device information such as the model, display resolution, Wi-Fi SSID, and MAC address, and retrieves commands from the attackers.

The malware supports the following nine commands:

  1. return – Retrieves a specified value from Android’s SharedPreferences storage
  2. copy – Copies stored or downloaded content to the device clipboard
  3. http – Sends HTTP GET or POST requests and can save part of the response
  4. web – Opens a URL in a WebView and executes supplied JavaScript
  5. loadlib – Not fully implemented when Kaspersky published the report
  6. loadlib2 – Downloads and executes arbitrary code or additional modules
  7. loadlib3 – Not fully implemented when Kaspersky published the report
  8. deeplink – Opens a specified resource in the browser
  9. traceroute – Checks whether specified hosts are reachable using ICMP ping

Kaspersky says the malware does not interfere with driving or critical vehicle control systems, and appears designed for advertising fraud and turning internet-connected car head units into residential proxy nodes for monetization purposes.
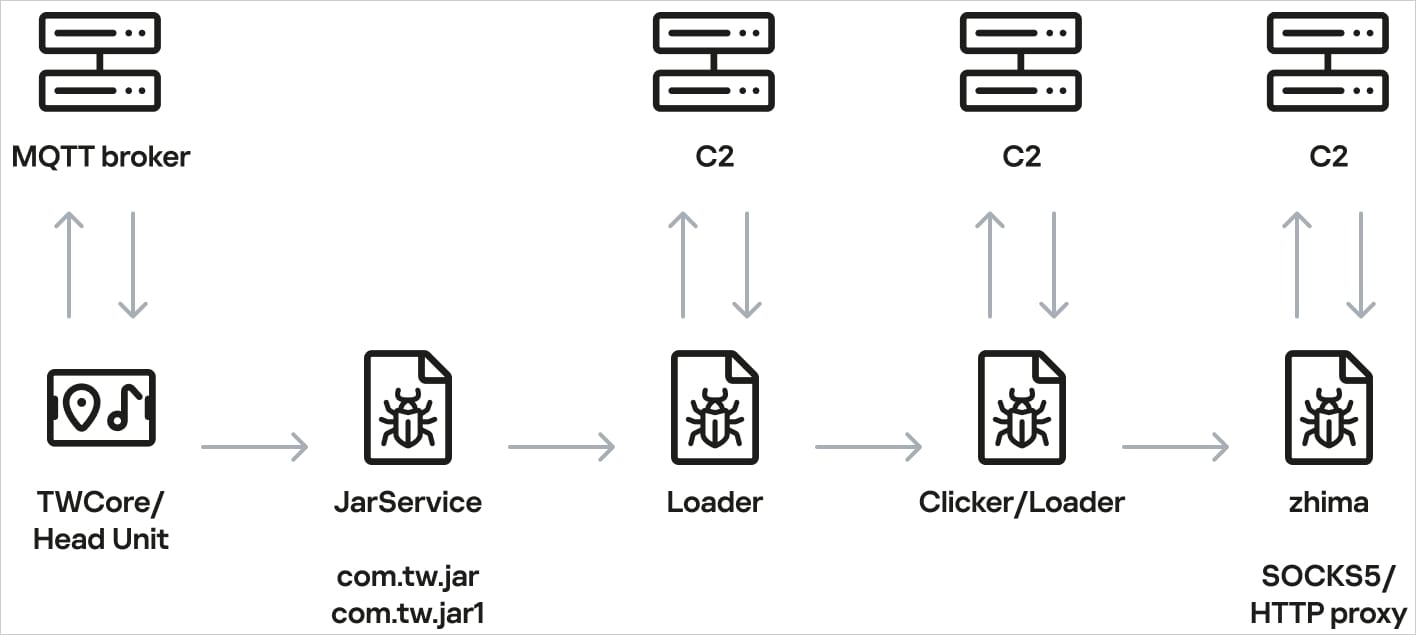
The head unit infection scheme
Source: Kaspersky

Researchers discovered that the operator primarily loaded a reverse-proxy module named ‘zhima,’ which turns the head unit into a proxy botnet node, and also made web requests for click-fraud activity.

Kaspersky says it notified DoFun of its findings, and the Chinese firm replied that it resolved the problem.

BleepingComputer has contacted both companies with questions about the initial compromise vector, and we will update the article with the information once received.

article image

Overall prevention scores can hide what happens after initial access. Once attackers are using valid credentials, prevention drops sharply.

The Blue Report 2026 measures defenses technique by technique across 338 million simulations run in customer production environments.

Get the report

Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
Previous ArticleMy Friend Is 21 Years Younger. She Taught Me to Stop Fearing Aging
Next Article XRP ETF inflows top $1.55 billion; XRP price rebounds; holders earn up to $9,000 daily
primereports
  • Website

Related Posts

Cybersecurity

Microsoft says September updates fix mouse settings reset issues

September 10, 2026
Cybersecurity

Infostealer Logs Expose Replayable AI Tokens That Can Bypass MFA

September 9, 2026
Cybersecurity

Microsoft Plugs Nearly 1,000 Security Holes – Krebs on Security

September 9, 2026
Add A Comment
Leave A Reply Cancel Reply

Top Posts

Threat of further violence looms after Mexican cartel rampage

February 25, 2026116 Views

‘Two-sided risk’ Medicare Advantage plans improve patient outcomes

February 24, 202673 Views

An $18bn settlement – and Zuckerberg barely blinked. The tech titans must be stripped of their power, and soon | Jonathan Freedland

August 28, 202626 Views
Stay In Touch
  • Facebook
  • YouTube
  • TikTok
  • WhatsApp
  • Twitter
  • Instagram
Latest Reviews

Subscribe to Updates

Get the latest tech news from FooBar about tech, design and biz.

PrimeReports.org
Independent global news, analysis & insights.

PrimeReports.org brings you in-depth coverage of geopolitics, markets, technology and risk – with context that helps you understand what really matters.

Editorially independent · Opinions are those of the authors and not investment advice.
Facebook X (Twitter) LinkedIn YouTube
Key Sections
  • World
  • Crypto
  • Cybersecurity
  • Geopolitics
  • Artificial Intelligence
  • Popular Now
All Categories
  • Artificial Intelligence
  • Climate Risks
  • Crypto
  • Cybersecurity
  • Defense
  • Economy
  • Geopolitics
  • Global Markets
  • Healthcare Innovation
  • Politics
  • Popular Now
  • Science
  • Technology
  • World
  • About Us
  • Contact Us
  • Privacy Policy
  • Terms & Conditions
  • Disclaimer
  • Cookie Policy
  • DMCA / Copyright Notice
  • Editorial Policy

Sign up for Prime Reports Briefing – essential stories and analysis in your inbox.

By subscribing you agree to our Privacy Policy. You can opt out anytime.
Latest Stories
  • Trump dangles $500 ACA refund checks, but legal basis is unclear
  • Guest post: How extreme heat is ‘creeping’ from summer into autumn and spring
  • Musk threatens to sue filmmaker Alex Gibney for defamation : NPR
© 2026 PrimeReports.org. All rights reserved.
Privacy Terms Contact

Type above and press Enter to search. Press Esc to cancel.