

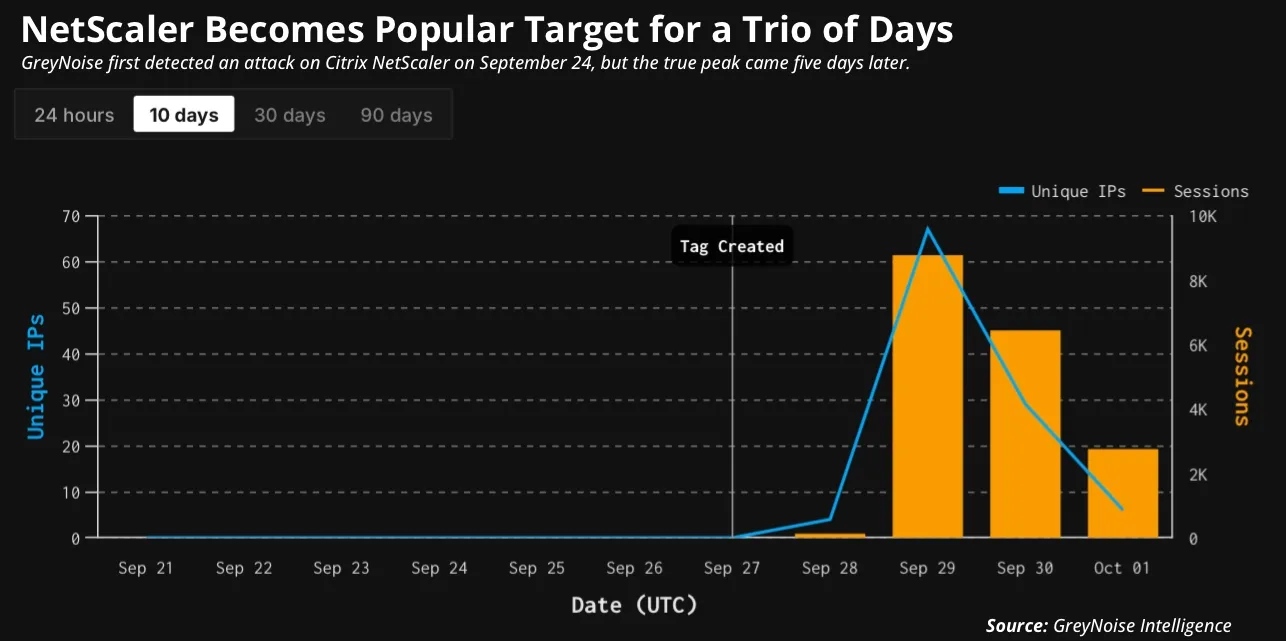
On Sept. 24, threat detection firm GreyNoise Intelligence observed a single US-based IP address scanning for Citrix NetScaler installations and conducting remote code execution (RCE) attacks. The company issued alerts to customers about the malicious activity.
Over the next two days, reports of potential zero-day attacks on NetScaler installations emerged on social media, and cybersecurity professionals debated whether the rumored attacks were true — some argued the activity targeted vulnerabilities already patched in August. On Sept. 26, however, Benjamin Harris, founder and CEO of exposure-management firm watchTowr, urged NetScaler users to take their systems offline.
“Monday will be too late,” he stated in a LinkedIn post.
By Sunday, Citrix seemingly agreed, posting an update that patched eight vulnerabilities (CVE-2026-88771 through CVE-2026-88778), including two zero-days that had been exploited in the wild. The blog post did not recommend taking servers offline until they were patched, instead urging customers to “upgrad[e to] the versions containing the fix immediately.” However, the two zero-days — CVE-2026-88771 and CVE-2026-88772 — came under widespread exploitation.
One Weekend, Two Disclosure Strategies
The same weekend, data protection provider Kiteworks took a different road.
On Sept. 25, the company issued a recommendation to customers, urging them to proactively take their systems offline based on intelligence about an imminent attack. With its engineering team and external national intelligence experts working together on identifying the security issue, the company warned that a zero-day attack could be coming. On Monday, Kiteworks published an advisory identifying the vulnerability with an update to patch it. In the end, the company determined the vulnerability would have affected only 1% of its customers, Kiteworks said in its statement.
“Telling customers to take production systems offline is not a decision any vendor makes lightly, and we knew exactly what we were asking of them,” Frank Balonis, the firm’s CISO, said in the statement. “We made it anyway, because when the choice is between certainty and convenience, customer data is not something we are willing to gamble with. That decision is what made the rest possible. We would make the same call again tomorrow to protect our customers’ data.”
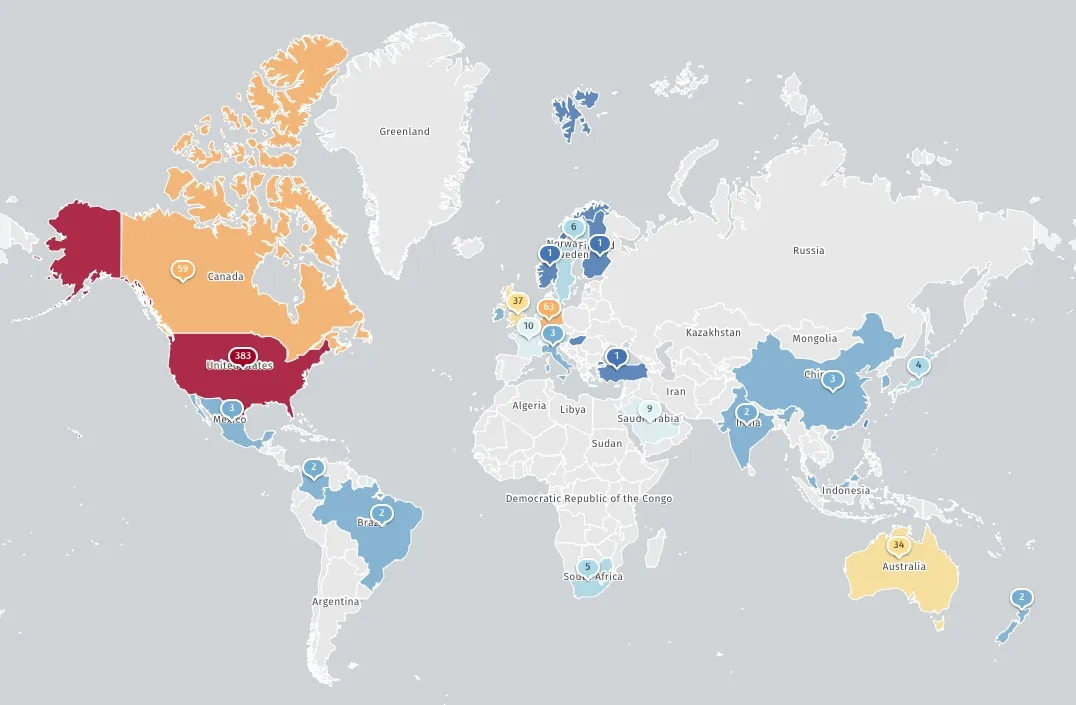
Kiteworks exposed IP addresses affect countries worldwide but are concentrated in the United States and Europe. Source: Shadowserver.org
The two approaches underscore the hazards for vendors that take aggressive defensive measures. Citrix’s response has come under fire from many in the cybersecurity community as being too little, too late. Why didn’t the company share intelligence sooner about the apparent zero-day attacks?
On the other hand, Kiteworks’ rare recommendation to shut down appliances could be considered overkill — especially since only 1% of customers were vulnerable — or an appropriately gauged response to a potentially significant attack targeting their customers, many of whom are government agencies or in regulated industries.
The decision to call for customers to shut down their systems was “wild,” according to John Strand, owner of Black Hills Information Security, a cybersecurity-training and penetration-testing firm.
“This isn’t an active attack — people aren’t actively being breached — and yet the vendor is telling customers to take their systems offline,” he said in a statement. “I’ve never heard of anything like this before. It remains to be seen whether Kiteworks is overreacting or whether this is exactly the right response, especially depending on how difficult the patch is to deploy.”
Shut Down or Stay Up?
For Kiteworks, the decision to tell customers to shut down their systems did not come easy, Jonathan Yaron, Kiteworks’ CEO and chairman, said in the company’s statement.
“The industry standard is to wait for proof of an attack,” he said. “We would rather be proactive on credible warning than wait for certainty and be too late. That is the standard we intend to keep.”
Unfortunately, security professionals had less information on the attacks on Citrix NetScaler: Some questioned whether the malicious activity targeted two vulnerabilities patched in August (CVE-2026-19490 and CVE-2026-19489). Citrix did not answer specific questions on the issue but pointed Dark Reading to its previous statement and security bulletin.
The company aimed to “immediately develop and release a new version of the software that addresses the issues,” Citrix stated through its spokesperson. “We always advise customers to promptly adopt the latest version of our software, and we are underscoring that guidance here to ensure our customers immediately benefit from the updates in this latest release.”
Even without a shutdown advisory from Citrix, suppliers and security teams were proactively telling NetScaler admins to take their appliances offline, citing a government warning, according to Satnam Narang, a senior staff research engineer at Tenable, which published an advisory on the issue.
“The shutdown conversation happened in both cases — it just came from different places,” Narang says.
No Easy Decisions for Vendors — or Customers
If another weekend brings the same decision, there is still no clear answer as to the right strategy, says Andrew Thompson, senior vice president of adversary operations at GreyNoise. While the company first detected activity against NetScaler appliances on Sept. 24, GreyNoise researchers did not initially connect the attack to specific CVEs.
“If early warning is from a credible source, they should act on it, [but] what’s considered to be acceptable action will vary from organization to organization,” Thompson says.
Tenable’s Narang notes that shutting down systems has a cost. Shuttering VPNs, for example, means cutting off access for remote workers, blocking access to applications that could impact customers, and shutting down data access that can disrupt operations.
“If vendors ask for it, they need to be specific about which customers and configurations are at risk, and how long the shutdown should last,” he says. “Kiteworks took down the systems it hosts and advised a nine-hour shutdown. A blanket ‘turn it off’ with no end date is hard to comply with.”
