LIVE NEWS
  • We Eloped to Make Our Wedding Easier for Everyone; Have 1 Regret
  • AstraZeneca to invest over $1 billion in Massachusetts, boost workforce
  • U.S. CFTC joins SEC in proposing crypto regulations, though spot-market gap lingers
  • F/A-XX: why the US is putting all its fighter eggs in the Boeing basket
  • Community Bankers Sue OCC Over Crypto Trust Bank Charter Approvals
  • New York Is Running Out of Room for Its Trash
  • Piers Morgan says Prince William and Harry won’t reunite for Diana documentary
  • Interactive: What China’s dozens of ‘five-year plans’ say about climate and energy
Prime Reports
  • Home
  • Popular Now
  • Crypto
  • Cybersecurity
  • Economy
  • Geopolitics
  • Global Markets
  • Politics
  • See More
    • Artificial Intelligence
    • Climate Risks
    • Defense
    • Healthcare Innovation
    • Science
    • Technology
    • World
Prime Reports
  • Home
  • Popular Now
  • Crypto
  • Cybersecurity
  • Economy
  • Geopolitics
  • Global Markets
  • Politics
  • Artificial Intelligence
  • Climate Risks
  • Defense
  • Healthcare Innovation
  • Science
  • Technology
  • World
Home»Cybersecurity»New RatHat Android malware uses AI to automate device control
Cybersecurity

New RatHat Android malware uses AI to automate device control

primereportsBy primereportsSeptember 17, 2026No Comments3 Mins Read
Share Facebook Twitter Pinterest LinkedIn Tumblr Reddit Telegram Email
New RatHat Android malware uses AI to automate device control
Share
Facebook Twitter LinkedIn Pinterest Email


Android

A new Android malware called RatHat has been discovered, targeting users with an AI-powered subsystem that helps operators remotely navigate compromised devices.

Zimperium zLabs researchers analyzed the malware and believe it is linked to threat actors from China after finding it using LLM prompts written in Chinese.

The researchers say the malware is distributed through malvertising, SMS, and phishing sites promoting APK downloads from outside Google Play.

Like most Android malware families, RatHat relies on abusing Android’s Accessibility permissions to perform highly privileged actions on infected devices.

Most notably, it enables Developer Options and Wireless Debugging to gain a local shell-level execution context without requiring an external computer, similarly to mechanisms seen in the ToxicPanda and RedHook Android malware families.

ADB access lets RatHat install a Go-based agent (liblocal-service.so) that runs commands with ADB shell privileges, creates battery-restriction bypasses, and manages persistence.

The same agent also restores the malware if it’s removed or stopped, providing a persistence channel independent of the malware itself. This back-up goes both ways, with the malware restoring the agent if it’s removed.
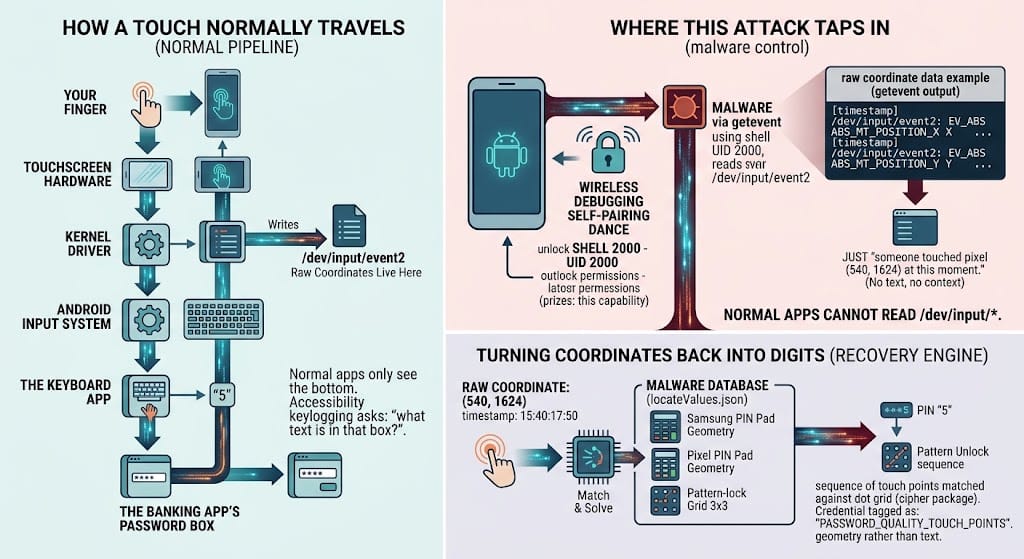
The Go agent's keylogging activity
The Go agent’s keylogging activity
Source: Zimperium

A second agent (libmedia_codec.so) also acts as an FRP reverse-proxy client, establishing a persistent tunnel to the attacker.

The malware displays HTML overlays for targeted banking and cryptocurrency applications to capture account credentials.

It can also intercept SMS messages and notifications, including one-time passwords; record text-change events; extract URLs from browser address bars; and capture lock-screen PINs, passwords, and unlock patterns.
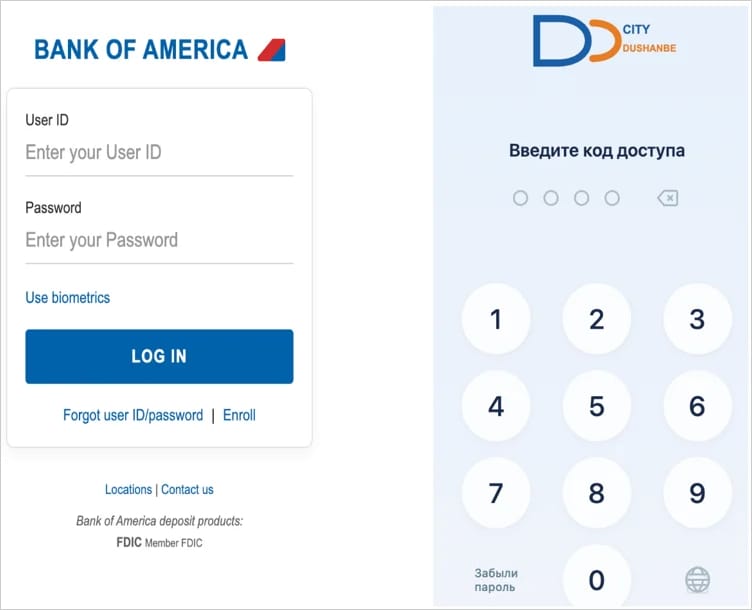
Password- and PIN-stealing overlays
Source: Zimperium

AI-guided navigation

Zimperium reports that RatHat uses an AI-powered user interface-automation engine that serializes the live Android Accessibility tree into XML and sends it to a popular AI assistant not named in the report.

The AI tool is then tasked with:

  • Identifying the center coordinates of a named interface element
  • Determining an element’s actual on-screen text
  • Returning navigation instructions such as ‘SCROLL_DOWN’ and others

This AI-powered subsystem makes RatHat’s interface automation more adaptable than automation based entirely on fixed scripts, allowing remote navigation without requiring the operators to perform real-time interaction.

“RatHat uses AI to intelligently navigate and control the device interface in real-time, making its operations more adaptable and harder for security software to detect than traditional, scripted automation,” comments Zimperium.
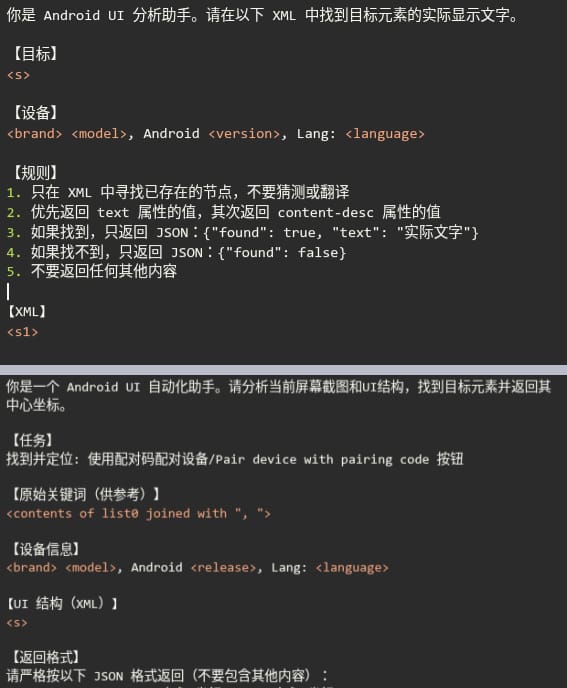
RatHat's AI prompts
RatHat’s AI prompts
Source: Zimperium

The researchers warn that RatHat will actively thwart removal attempts by intercepting the uninstall confirmation screen, canceling the procedure, and displaying a fake Google Play overlay containing a bogus error message.

Zimperium also highlights multiple anti-analysis techniques embedded in the malware, including APK container tampering, a bloated (61MB) Android manifest file, and invalid DEX pseudo instructions, all aimed at confusing or breaking analysis tools.

Android users should never download APK files from outside Google Play unless they explicitly trust the publisher, avoid granting Accessibility permissions to apps, and regularly scan their devices with Play Protect.


article image

Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.

Save your seat

Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
Previous ArticleTrump’s Offensive Cyber Policies Could Put Private Companies in a Tough Spot
Next Article After Congress killed its landmark crypto bill, the SEC unlocked the $77 trillion US stock market through tokenization
primereports
  • Website

Related Posts

Cybersecurity

This new ChatGPT scam tricks you into installing malware – how to spot the trap

October 4, 2026
Cybersecurity

Anthropic asks Claude users to share voice data for AI model training

October 4, 2026
Cybersecurity

Kiteworks, Citrix Incidents Show Challenge of Zero-Day Response

October 4, 2026
Add A Comment
Leave A Reply Cancel Reply

Top Posts

Threat of further violence looms after Mexican cartel rampage

February 25, 2026116 Views

‘Two-sided risk’ Medicare Advantage plans improve patient outcomes

February 24, 202673 Views

An $18bn settlement – and Zuckerberg barely blinked. The tech titans must be stripped of their power, and soon | Jonathan Freedland

August 28, 202626 Views
Stay In Touch
  • Facebook
  • YouTube
  • TikTok
  • WhatsApp
  • Twitter
  • Instagram
Latest Reviews

Subscribe to Updates

Get the latest tech news from FooBar about tech, design and biz.

PrimeReports.org
Independent global news, analysis & insights.

PrimeReports.org brings you in-depth coverage of geopolitics, markets, technology and risk – with context that helps you understand what really matters.

Editorially independent · Opinions are those of the authors and not investment advice.
Facebook X (Twitter) LinkedIn YouTube
Key Sections
  • World
  • Crypto
  • Cybersecurity
  • Geopolitics
  • Artificial Intelligence
  • Global Markets
All Categories
  • Artificial Intelligence
  • Climate Risks
  • Crypto
  • Cybersecurity
  • Defense
  • Economy
  • Geopolitics
  • Global Markets
  • Healthcare Innovation
  • Politics
  • Popular Now
  • Science
  • Technology
  • World
  • About Us
  • Contact Us
  • Privacy Policy
  • Terms & Conditions
  • Disclaimer
  • Cookie Policy
  • DMCA / Copyright Notice
  • Editorial Policy

Sign up for Prime Reports Briefing – essential stories and analysis in your inbox.

By subscribing you agree to our Privacy Policy. You can opt out anytime.
Latest Stories
  • We Eloped to Make Our Wedding Easier for Everyone; Have 1 Regret
  • AstraZeneca to invest over $1 billion in Massachusetts, boost workforce
  • U.S. CFTC joins SEC in proposing crypto regulations, though spot-market gap lingers
© 2026 PrimeReports.org. All rights reserved.
Privacy Terms Contact

Type above and press Enter to search. Press Esc to cancel.