

Tech giants General Electric (GE) and Philips have also confirmed they’re investigating claims that the Clop ransomware gang breached their systems and stole data.
While a GE spokesperson said the company is aware of the claim and is “working to assess the potential issue,” a Philips spokesperson confirmed its systems were breached but said the incident has been contained and didn’t affect customers.
“Philips has identified and contained an attempted cybersecurity compromise of a specific enterprise server related to internal data,” Philips said in a statement shared with Reuters. “This has no impact on customer environments.”
GE and Philips spokespersons have yet to reply after BleepingComputer also reached out to them for more details and to confirm the Clop ransomware gang’s claims.
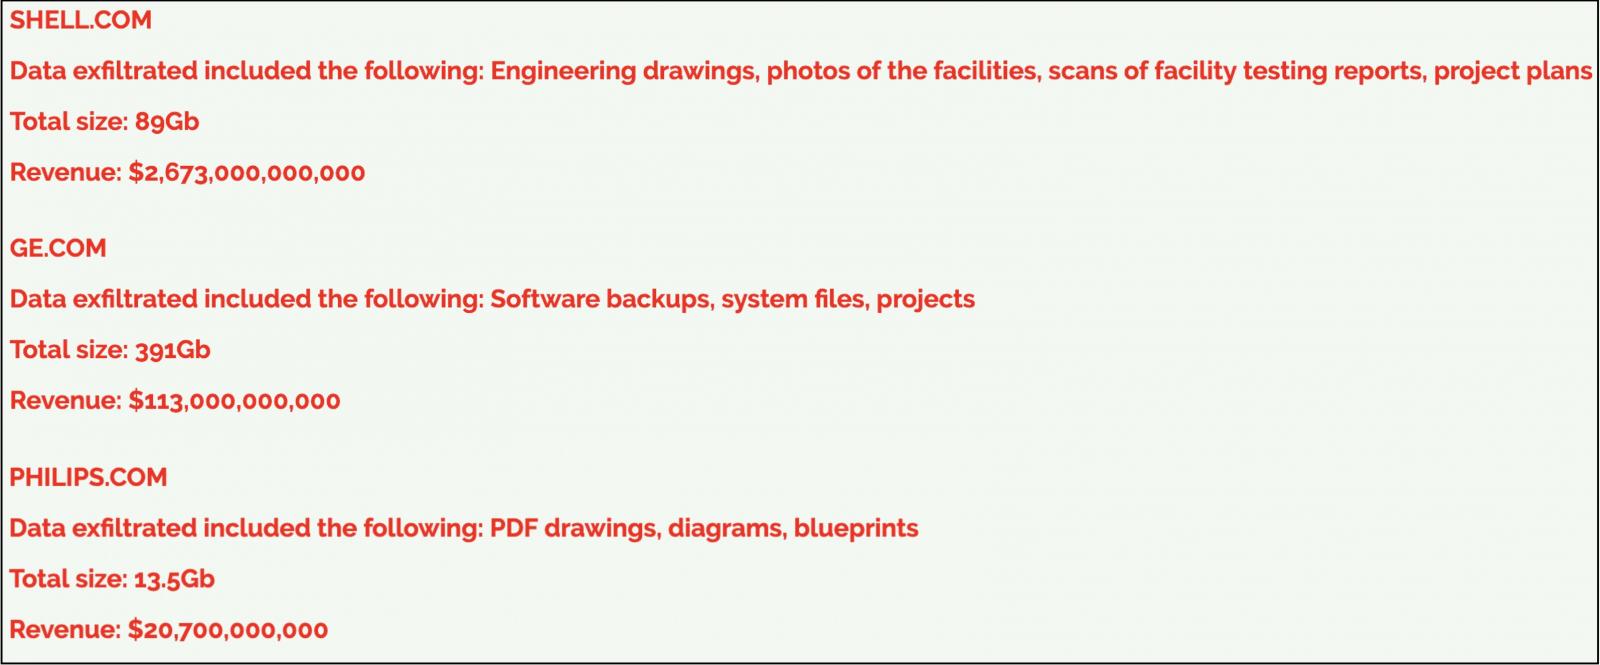
This comes after oil giant Shell also said on Friday that it is investigating a potential security incident after the Clop hacking group claimed it stole 89GB of data.
“We are aware of a potential incident,” a Shell spokesperson told BleepingComputer when asked to confirm the gang’s data theft claims. “We are working with our security teams and relevant experts to investigate.
While the three companies have yet to share more information, the Clop gang has listed them on its leak site as part of a batch of 43 new victims likely targeted in data theft attacks exploiting a critical improper input validation vulnerability (tracked as CVE-2026-12569) against Internet-exposed PTC Windchill and PTC FlexPLM instances.
PTC says the two enterprise software platforms are widely used by high-profile companies across the aerospace, defense, automotive, heavy machinery, retail, and medtech sectors. The company says more than 30,000 customers globally use its products, including over 1,500 brand and retail customers using FlexPLM.
In these attacks, Clop claims it stole a wide range of sensitive data from the companies’ compromised systems, including backups, project plans, photos of facilities, drawings, diagrams, blueprints, and more, belonging to Shell, GE, and Philips.
PTC began releasing CVE-2026-12569 security patches on June 17 and urged customers to review environments for indicators of compromise (IOCs) in a private advisory, even though there was no confirmation of in-the-wild exploitation.
Since then, cybersecurity company ReliaQuest and the Ransomware Information Sharing and Analysis Centre (Ransom-ISAC) have confirmed Clop’s Windchill and FlexPLM attacks, in which the threat actors have been deploying JSP webshells to steal sensitive data from victims’ compromised PLM platforms.
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) also confirmed that the flaw is actively exploited in attacks after PTC warned of “heightened threat activity” on June 26, mandating federal agencies to secure their PTC Windchill and FlexPLM instances within three days after adding it to its catalog of known exploited vulnerabilities.
This vulnerability has also prompted emergency action from German authorities, with the Federal Office for Information Security (BSI) warning PTC customers in the middle of the night to patch systems as quickly as possible.
The Clop extortion gang has a long history of targeting enterprise platforms in data theft attacks, breaching Accellion FTA, GoAnywhere MFT, SolarWinds Serv-U FTP, Cleo, and MOVEit Transfer file-sharing servers in previous campaigns, with the latter affecting over 2,770 organizations worldwide.
Starting in early August 2025, it also began exploiting an Oracle EBS zero-day flaw to steal sensitive files from many organizations. The list of victims includes many high-profile organizations worldwide, including The Washington Post, GlobalLogic, Harvard University, the University of Pennsylvania, Logitech, Estée Lauder, Korean Air, and American Airlines subsidiary Envoy Air.
The U.S. Department of State now offers a $10 million reward for any information linking the cybercrime gang’s attacks to a foreign government.
Overall prevention scores can hide what happens after initial access. Once attackers are using valid credentials, prevention drops sharply.
The Blue Report 2026 measures defenses technique by technique across 338 million simulations run in customer production environments.
