
LIVE NEWS
  • Ban on neo-Nazi White Australia party is ‘authoritarian’ and breaches constitution, high court hears | Australia news
  • Dell Says AI Will Drive 75 Percent Of Datacenter Demand By 2030
  • London talks raise hopes for green shipping deal
  • Novo Nordisk stops two cardiovascular studies aimed at lowering inflammation
  • Orionx Halts Withdrawals and Winds Down After Alleged $7M Asset Transfers
  • UN Resolution 2758: when interpretation becomes institutional power
  • Reading sci-fi could help us plan for futures stranger than fiction
  • Capital B Raises €25.3M And Buys 376 Bitcoin For Treasury
Prime Reports
  • Home
  • Popular Now
  • Crypto
  • Cybersecurity
  • Economy
  • Geopolitics
  • Global Markets
  • Politics
  • See More
    • Artificial Intelligence
    • Climate Risks
    • Defense
    • Healthcare Innovation
    • Science
    • Technology
    • World
Prime Reports
  • Home
  • Popular Now
  • Crypto
  • Cybersecurity
  • Economy
  • Geopolitics
  • Global Markets
  • Politics
  • Artificial Intelligence
  • Climate Risks
  • Defense
  • Healthcare Innovation
  • Science
  • Technology
  • World
Home»Cybersecurity»How attackers hosted a fake Claude download page on the claude.ai domain
Cybersecurity

How attackers hosted a fake Claude download page on the claude.ai domain

primereportsBy primereportsJuly 23, 2026No Comments3 Mins Read
Share Facebook Twitter Pinterest LinkedIn Tumblr Reddit Telegram Email
How attackers hosted a fake Claude download page on the claude.ai domain
Share
Facebook Twitter LinkedIn Pinterest Email


A threat actor abused Anthropic’s Claude Artifacts feature to funnel users toward malware, Huntress researchers have disclosed.

Employees at at least 29 organizations were compromised over two days in July, after searching for the Claude desktop app and clicking a sponsored Bing ad.

The ad pointed to the genuine claude.ai domain, but landed on an attacker-published public artifact, which redirected them to a spoofed download site serving SectopRAT.

What are Claude Artifacts?

Artifacts are a Claude.ai feature that renders certain content such as code, documents, diagrams, or full web pages in a panel beside the chat rather than as text in the conversation.

More importantly, users can publish an artifact to a public link, letting anyone view it without a Claude account.

In this particular case, the artifact to which potential victims were directed rendered a fully functional page that looked like a legitimate Claude download page, and the fact that it was hosted on the Claude.ai domain completed the illusion.

The only thing revealing its true nature was a short sentence displayed in the upper left corner, saying: “Content is user-generated and unverified.” However, this disclaimer is easily missed.
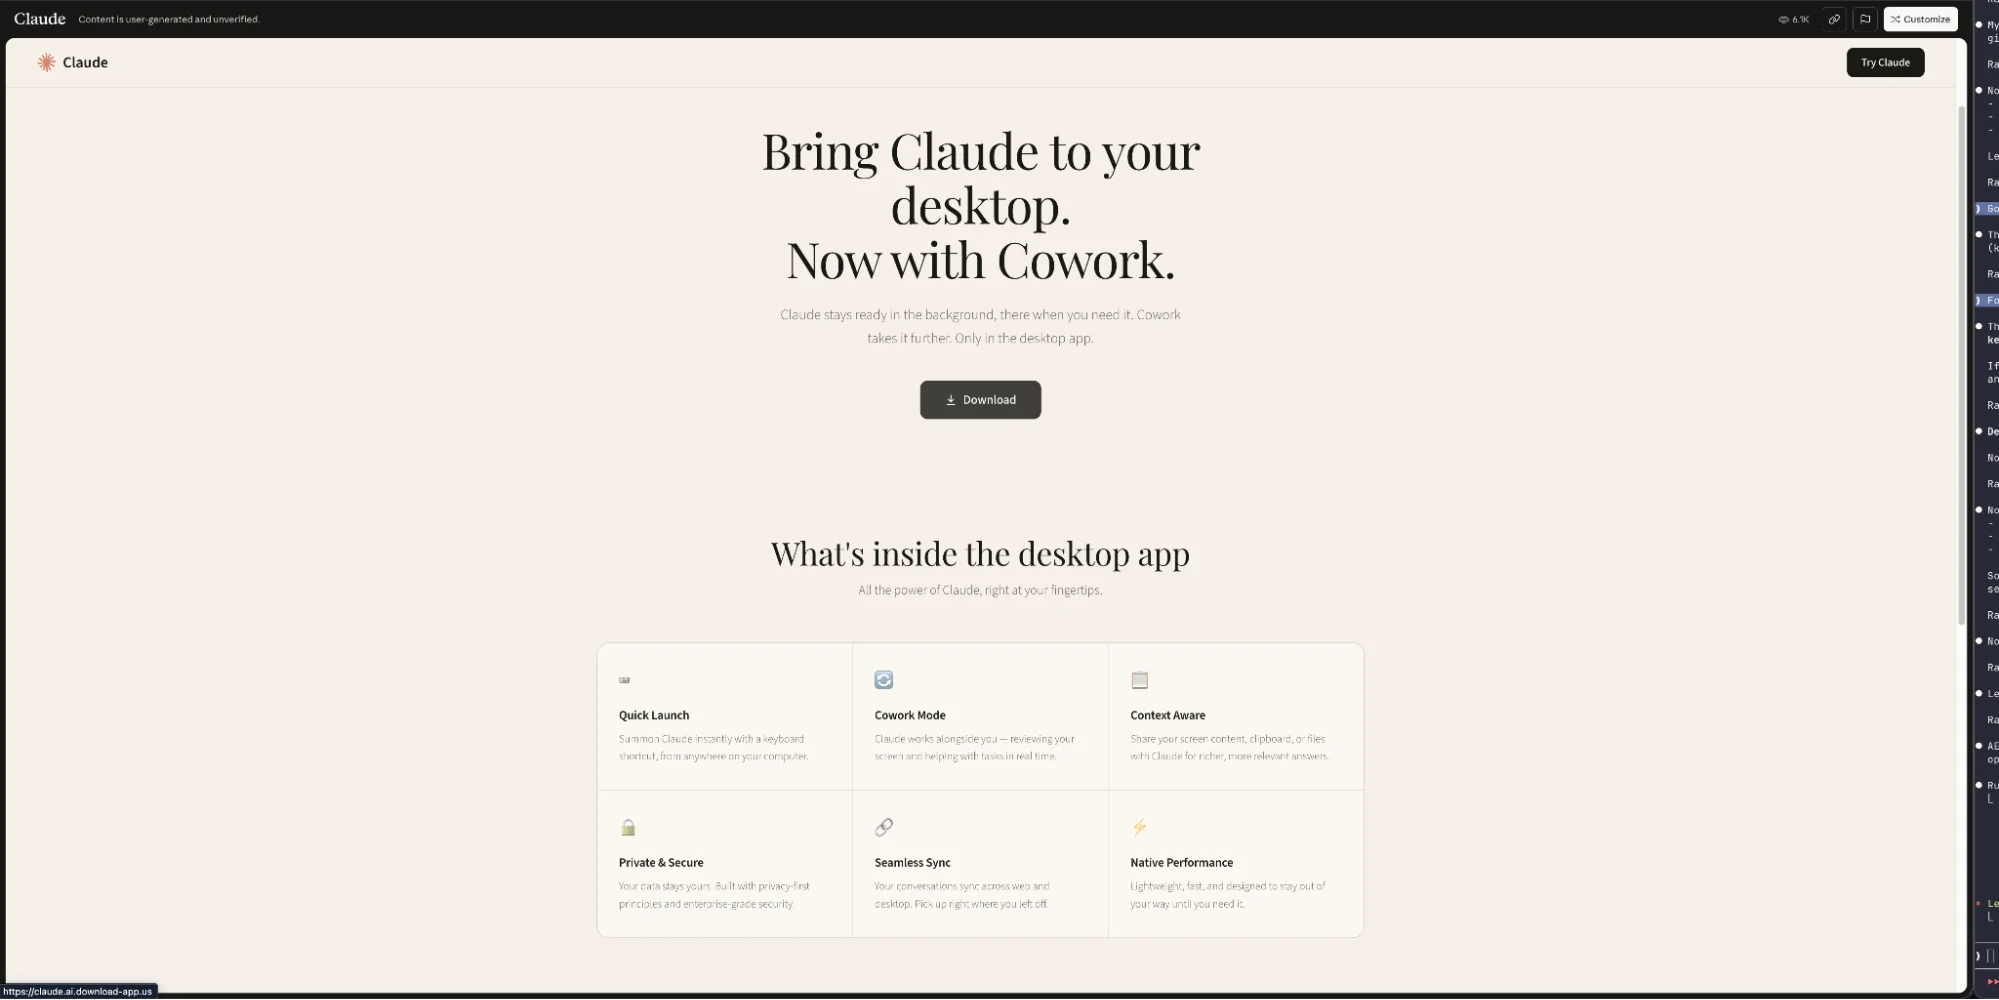
Claude Artifacts download malware

The Claude Artifact showing the fake download page (Source: Huntress)

Huntress reported the artifact to Anthropic and it was taken down before the company published its findings on July 22. By then, the page had been viewed 7,100 times.

Delivering the malware

Clicking on the “Download” button redirected victims to an external domain, first claude.ai.download-app[.]us and subsequently downloading-api.it[.]com/html/claude/win, from which they downloaded a bundle.

It contained a renamed (but legitimate) signed JetBrains binary vulnerable to DLL sideloading, a tampered libcef.dll carrying the actual malware, and an executable (DockerDesktop.exe) that’s dropped to disk and registered as a scheduled task so that it can keep reinfecting the machine.

The malware is SectopRAT, a remote access trojan (RAT) that grabs and exfiltrates user credit card data, personal information, files, and passwords.

Tracing the operator

The attacker had layered several defences on top of the payloads, and Huntress researchers had to go through considerable effort (and use Claude) to analyze them and unearth the command-and-control address.

In the end, they discovered connections to previous malware delivery campaigns.

WHOIS records and the Validin intelligence platform tied the download-app[.]us registration to an email address linked to ten domains going back to December 2025. One of them, polse[.]us, was seized by Microsoft as part of Operation Endgame after being identified as hosting the StealC infostealer.

Huntress also connected the actor to an April 2026 campaign that used Docker Hub to distribute a fake Docker Desktop installer. That campaign employed the same libcef.dll sideloading trick, and also relied on a trusted domain to disarm suspicion. (And this explains the leftover DockerDesktop.exe filename in this month’s bundle.)

Their advice for users is not to trust search engine ads and top-level domains implicitly when searching for software to download, as threat actors have become experts in pushing malicious ads via popular search engines and finding ways to host malicious content on legitimate platforms and domains.

Subscribe to our breaking news e-mail alert to never miss out on the latest breaches, vulnerabilities and cybersecurity threats. Subscribe here!

Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
Previous ArticleTrump to impose double-digit tariffs on dozens of countries : NPR
Next Article How the Houthi Red Sea blockade will impact the world | Politics
primereports
  • Website

Related Posts

Cybersecurity

Magento StyleSmuggler zero-day exploited to deploy Linux backdoor

September 7, 2026
Cybersecurity

Attackers Hijack MikroTik Routers Through Internet-Exposed SSH Without Authentication

September 6, 2026
Cybersecurity

Week in review: Claude accounts compromised through infostealer, Patch Tuesday forecast

September 6, 2026
Add A Comment
Leave A Reply Cancel Reply

Top Posts

Threat of further violence looms after Mexican cartel rampage

February 25, 2026116 Views

‘Two-sided risk’ Medicare Advantage plans improve patient outcomes

February 24, 202673 Views

An $18bn settlement – and Zuckerberg barely blinked. The tech titans must be stripped of their power, and soon | Jonathan Freedland

August 28, 202626 Views
Stay In Touch
  • Facebook
  • YouTube
  • TikTok
  • WhatsApp
  • Twitter
  • Instagram
Latest Reviews

Subscribe to Updates

Get the latest tech news from FooBar about tech, design and biz.

PrimeReports.org
Independent global news, analysis & insights.

PrimeReports.org brings you in-depth coverage of geopolitics, markets, technology and risk – with context that helps you understand what really matters.

Editorially independent · Opinions are those of the authors and not investment advice.
Facebook X (Twitter) LinkedIn YouTube
Key Sections
  • World
  • Crypto
  • Cybersecurity
  • Geopolitics
  • Artificial Intelligence
  • Popular Now
All Categories
  • Artificial Intelligence
  • Climate Risks
  • Crypto
  • Cybersecurity
  • Defense
  • Economy
  • Geopolitics
  • Global Markets
  • Healthcare Innovation
  • Politics
  • Popular Now
  • Science
  • Technology
  • World
  • About Us
  • Contact Us
  • Privacy Policy
  • Terms & Conditions
  • Disclaimer
  • Cookie Policy
  • DMCA / Copyright Notice
  • Editorial Policy

Sign up for Prime Reports Briefing – essential stories and analysis in your inbox.

By subscribing you agree to our Privacy Policy. You can opt out anytime.
Latest Stories
  • Ban on neo-Nazi White Australia party is ‘authoritarian’ and breaches constitution, high court hears | Australia news
  • Dell Says AI Will Drive 75 Percent Of Datacenter Demand By 2030
  • London talks raise hopes for green shipping deal
© 2026 PrimeReports.org. All rights reserved.
Privacy Terms Contact

Type above and press Enter to search. Press Esc to cancel.