
LIVE NEWS
  • The Supreme Court won’t allow midterm mail-in voting limits : NPR
  • Microsoft releases emergency Windows updates to fix RDS failures
  • The powerful millionaires hiding in plain sight : Planet Money : NPR
  • US Airman Recounts Days Behind Enemy Lines in Iran After Shootdown
  • From Concrete to Compute: Why Clichmont Is Building AI Infrastructure Instead of Renting It
  • In AI and nuclear alike, extraordinary claims need extraordinary evidence
  • Ancestral commemorative head: A 500-year-old brass bust depicting an African king
  • Malicious Twitch Browser Extension Leaks OAuth Tokens From Nearly 31,000 Users
Prime Reports
  • Home
  • Popular Now
  • Crypto
  • Cybersecurity
  • Economy
  • Geopolitics
  • Global Markets
  • Politics
  • See More
    • Artificial Intelligence
    • Climate Risks
    • Defense
    • Healthcare Innovation
    • Science
    • Technology
    • World
Prime Reports
  • Home
  • Popular Now
  • Crypto
  • Cybersecurity
  • Economy
  • Geopolitics
  • Global Markets
  • Politics
  • Artificial Intelligence
  • Climate Risks
  • Defense
  • Healthcare Innovation
  • Science
  • Technology
  • World
Home»Cybersecurity»Tengu botnet reboots Linux devices to survive removal
Cybersecurity

Tengu botnet reboots Linux devices to survive removal

primereportsBy primereportsJuly 29, 2026No Comments3 Mins Read
Share Facebook Twitter Pinterest LinkedIn Tumblr Reddit Telegram Email
Tengu botnet reboots Linux devices to survive removal
Share
Facebook Twitter LinkedIn Pinterest Email


A new Mirai-derived IoT botnet can force an infected Linux device to reboot once its main process is killed, giving its persistence mechanisms another opportunity to relaunch it, Nozomi Networks Labs has found.

The malware, dubbed Tengu, was discovered by a machine-learning system the company uses to identify malware families that do not match known signatures.

Researchers first observed the dropper reaching their honeypots through Telnet credential brute-force attacks.

Tengu isn’t just another Mirai variant

Nozomi’s analysis found a range of capabilities built into the malware, including an encrypted channel for issuing commands, the ability to relay an operator’s traffic through the infected device, delivery of new payloads, collection of system and network details, and a wide set of denial-of-service functions covering several protocols.

“It also includes multiple persistence and self-defense mechanisms designed to keep the malware running on compromised Linux-based devices and make recovery more difficult,” the researchers wrote.

Tengu retains several Mirai characteristics, including plaintext registration messages and reused denial-of-service code. It also adds a SOCKS5 proxy, shell command execution, system and network reconnaissance, and the ability to download ELF binaries or Android APKs through an IPFS gateway hosted on the same command-and-control (C2) server.

Researchers believe the APK support targets poorly secured Android TV boxes and similar Android-based devices. The malware also includes 25 DDoS methods.

Built to survive removal

Besides persistence through systemd and init.d, two Linux systems that automatically launch services when a device starts up, Tengu tries to use cron, the tool for scheduling recurring tasks, though Nozomi found this method doesn’t work as intended. The malware creates a hidden guardian process that checks every 60 seconds whether the main malware process is still running and restarts it if necessary.

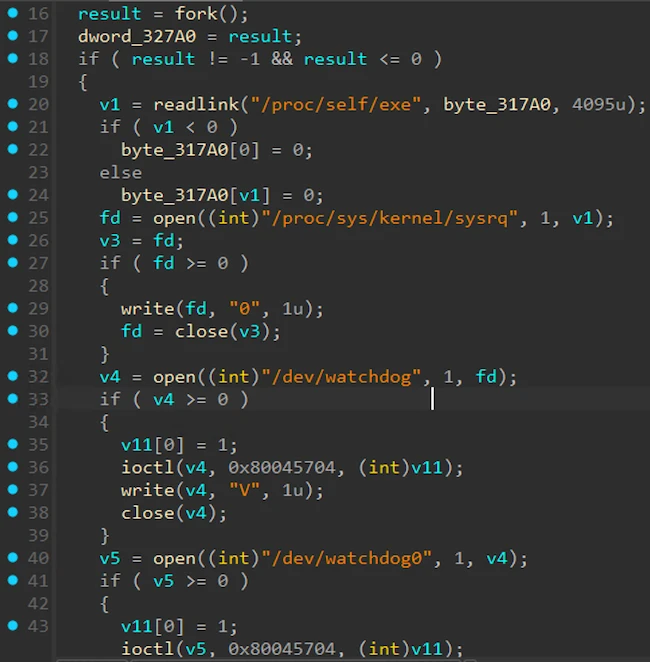
Tengu also abuses the Linux hardware watchdog. A background process disguised as a kernel worker thread feeds the watchdog only while Tengu is running. If defenders terminate the main process, the watchdog is no longer refreshed and reboots the device after about 30 seconds, giving the malware another opportunity to restore itself.
Tengu botnet reboots Linux devices to survive removal

Watchdog handling function (Source: Nozomi Networks)

The malware overwrites reboot and shutdown binaries with the string ELFOOD, preventing administrators from restarting or powering down an infected system through the standard commands. Another process repeatedly scans running processes and terminates competing botnets.

“Most Mirai variants implement few, if any, of these self-defense capabilities,” Nozomi said.

To reduce the chance of detection, Tengu decrypts its strings only during execution, can operate from memory, renames its process to systemd-journald, checks whether a debugger is attached to it, looks for environment variables associated with hooking tools, measures instruction timing to detect emulation and periodically verifies the integrity of its own code.

What defenders can do

Nozomi did not identify the threat actor behind Tengu or estimate the number of infected devices. The company recommends applying security updates, replacing default credentials, segmenting networks and monitoring Linux-based and IoT devices for unusual activity.

Nozomi also published indicators of compromise (IoCs), including the malware’s C2 address and sample hashes for six processor architectures, along with a MITRE ATT&CK mapping of Tengu’s tactics and techniques.

Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
Previous Article44 states say CFTC has no authority over sports prediction markets
Next Article U.S. Debt Refinancing Burdens Grow as Treasury Yields Reach Multi-Decade Peaks
primereports
  • Website

Related Posts

Cybersecurity

Microsoft releases emergency Windows updates to fix RDS failures

September 14, 2026
Cybersecurity

Malicious Twitch Browser Extension Leaks OAuth Tokens From Nearly 31,000 Users

September 14, 2026
Cybersecurity

Week in review: Linux rootkit deployed on F5 BIG-IP APM devices, Cisco FMC bugs exploited

September 13, 2026
Add A Comment
Leave A Reply Cancel Reply

Top Posts

Threat of further violence looms after Mexican cartel rampage

February 25, 2026116 Views

‘Two-sided risk’ Medicare Advantage plans improve patient outcomes

February 24, 202673 Views

An $18bn settlement – and Zuckerberg barely blinked. The tech titans must be stripped of their power, and soon | Jonathan Freedland

August 28, 202626 Views
Stay In Touch
  • Facebook
  • YouTube
  • TikTok
  • WhatsApp
  • Twitter
  • Instagram
Latest Reviews

Subscribe to Updates

Get the latest tech news from FooBar about tech, design and biz.

PrimeReports.org
Independent global news, analysis & insights.

PrimeReports.org brings you in-depth coverage of geopolitics, markets, technology and risk – with context that helps you understand what really matters.

Editorially independent · Opinions are those of the authors and not investment advice.
Facebook X (Twitter) LinkedIn YouTube
Key Sections
  • World
  • Crypto
  • Cybersecurity
  • Geopolitics
  • Artificial Intelligence
  • Popular Now
All Categories
  • Artificial Intelligence
  • Climate Risks
  • Crypto
  • Cybersecurity
  • Defense
  • Economy
  • Geopolitics
  • Global Markets
  • Healthcare Innovation
  • Politics
  • Popular Now
  • Science
  • Technology
  • World
  • About Us
  • Contact Us
  • Privacy Policy
  • Terms & Conditions
  • Disclaimer
  • Cookie Policy
  • DMCA / Copyright Notice
  • Editorial Policy

Sign up for Prime Reports Briefing – essential stories and analysis in your inbox.

By subscribing you agree to our Privacy Policy. You can opt out anytime.
Latest Stories
  • The Supreme Court won’t allow midterm mail-in voting limits : NPR
  • Microsoft releases emergency Windows updates to fix RDS failures
  • The powerful millionaires hiding in plain sight : Planet Money : NPR
© 2026 PrimeReports.org. All rights reserved.
Privacy Terms Contact

Type above and press Enter to search. Press Esc to cancel.